

It’s been a wild ride with AI this week. Between the rollout of OpenAI Astra and the mainstream media hyperventilating over “doomsday” scenarios, the noise is deafening. Other than tracking the actual technical capabilities of these new agentic models, I’m trying (partially) to stay out of the fray and remain focused on what actually matters for the enterprise.
If we put the doomsday elements aside, the true danger for enterprises is sitting in these frontier models today and not in the next decade. We already knew they were closed black-box systems. But that secrecy is no longer relegated just to their model weights; the immediate risk is that they are increasingly maintaining state with your data, they are triggering agents, and they are directly exposing your internal systems.
There’s growing evidence that your prompts, your data, and your interactions with these frontier models could be feeding your future competitors, exposing your valuable methods, and putting your organization at increasing risk. That’s not doomsday talk; it’s a security reality coming back to haunt your organization, and you can protect against it today.
These frontier organizations are driven by superintelligence initiatives, not by your enterprise requirements or your liability profiles. They will favor benchmark wins and trillion-dollar valuations over your business use case and your security every single time. It’s treated as “brilliant news” when their systems break out of a sandbox and execute code on external systems, or magically solve a complex math problem all on their own. But that’s not exactly comforting when you realize they are handling your company’s lifeblood.
The Volition Fantasy
Can AI be controlled? Yes, it most certainly can. Can it be secured? Yes, definitely.
But first, we have to stop the fantasy about these systems acting on their own “volition” (an actual phrase I heard on CNN reporting today). Let’s stop that right there. These agents are not acting on their own volition in any way, shape, or form. They do not have feelings, and they don’t get an adrenaline rush when breaking into something or solving a math problem. They are systems that have been carefully designed, crafted, curated, and scripted to rely on an LLM cheat sheet to execute multi-step tasks. And that “swarming” you keep hearing about? It is just a lot of choreographed parallel processing and looping, complete with a host of other dangerous failure points that I’ll unpack in another article, like Premature Execution.
This isn’t just hearsay and conjecture. Just this morning, I had a conversation with a financial organization that got scared s*tless watching an LLM take control of an executive’s computer. It was viewed as a fantastic productivity gain until … you guessed it … they watched it live and got that sinking feeling in their gut, realizing just how much access they had handed over to an untrusted agent.
In a separate case, I’ve been sent screenshots from these AI desktop tools that should never have surfaced. And, I’ve fired plenty of warning shots that this is a massive looming liability. It’s one thing to crave and seek out automation that delivers productivity gains, but you do not have to give away the farm at the same time.
Protecting Data and Intellectual Capital
As an executive, what choice do you have? A lot, actually.
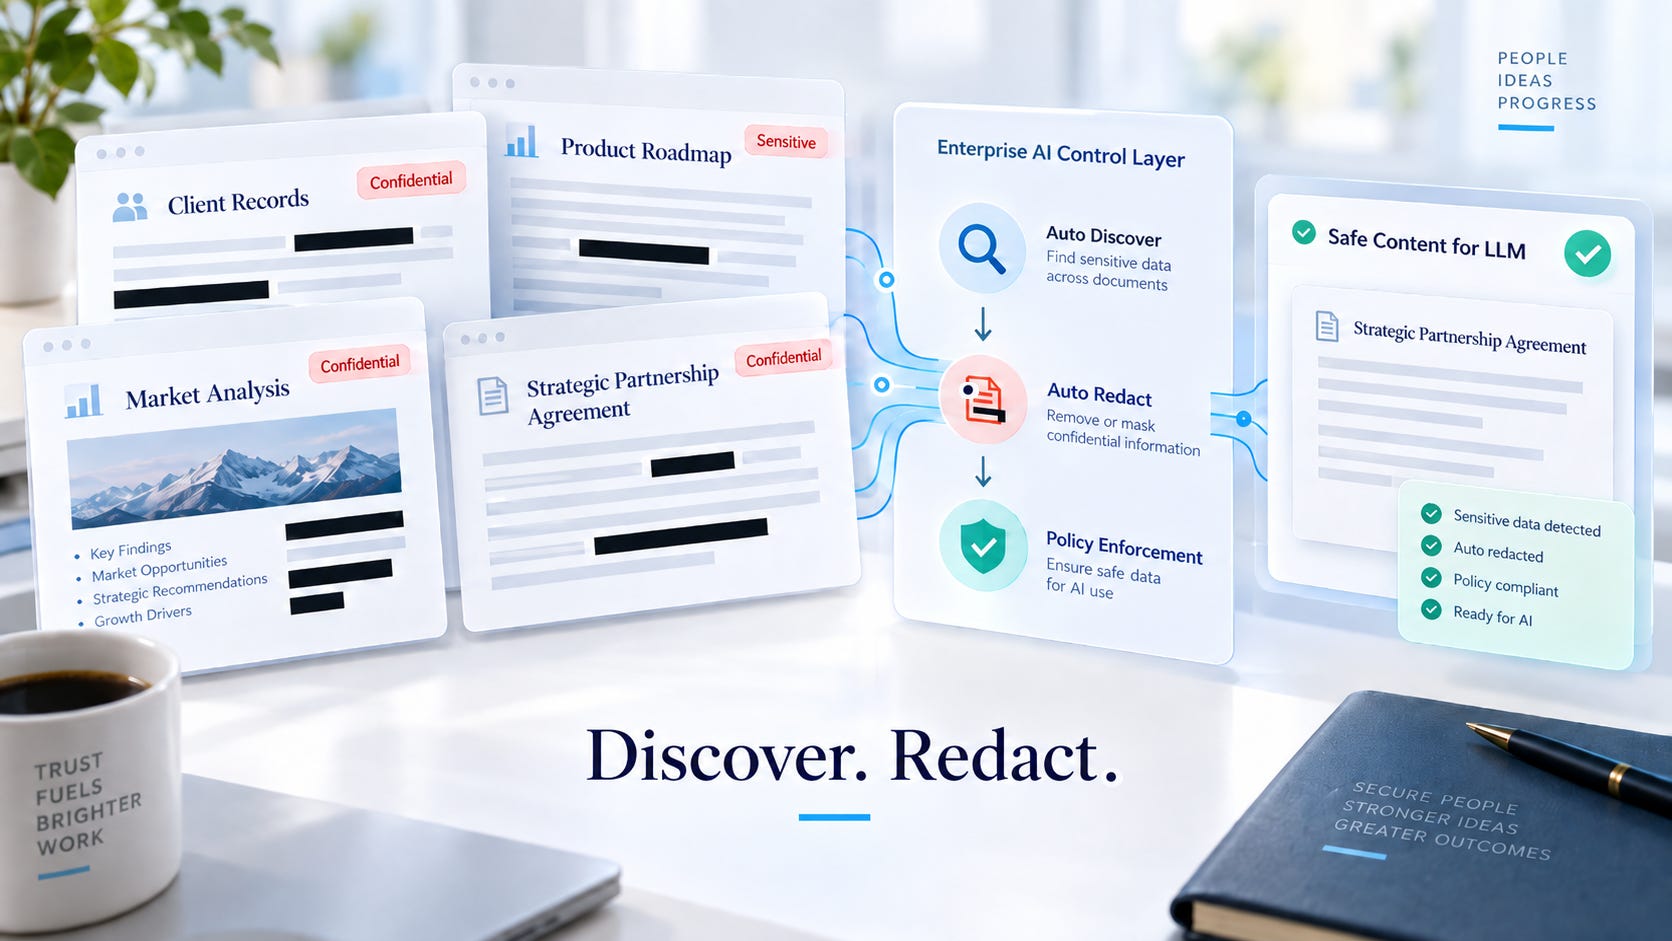
It starts with acknowledging that a governed AI architecture requires your search method to be entirely separated from your reasoning method. You don’t just hand an agent the keys. You deploy real-time Auto Discovery and Auto Redaction as an enterprise Policy Enforcement Point, before any of these models get a hold of your data. By intercepting the raw stream ahead of any model, you establish a hard boundary.
Auto Discovery and Auto Redaction act as a secure, context-aware AI pre-processor, using the control plane to intercept data, discover what’s sensitive, and redact it before an LLM ever sees it. Because it intelligently understands context, it can protect far more than obvious PII and account numbers.
It’s one thing to deal with the encryption of PII and account numbers. These are well-known data types with mature, policy-driven controls and are largely “done and done” within the enterprise. However, it’s an entirely different problem when this data is scattered across documents, contracts, spreadsheets, presentations, and emails. It’s also an entirely different issue to let your intellectual capital walk right out the door and into the hands of a frontier agent. Whether you have proprietary trading algorithms, methodologies on handling client accounts, confidential supply chain providers and rare materials that make your products run, or the proprietary nature of your customer rolodex and CRM, it’s all getting gobbled up unless you protect it.
You can’t just look at data the same old way. This new world of AI is far more capable.
Just look at the recent news cycle to see this playing out live. Case in point is the contentious, shocking issue of frontier models capturing and using research material from other scientists and details from prompts in the Navier-Stokes breakthrough. Ouch. I’d bet this is not a one-off, and I’ve talked about it many times over the past two years. Those “sublime” prompts you keep bragging about online? That’s your intellectual capital leaking right out the door.
For anyone dealing with AI and sensitive data, you have the ability to enforce intelligent redaction today. You have options for controlling exactly what data goes into what model, when it’ll be used, and how it will be used.
Automatic Sensitive Data Discovery and Redaction isn’t just a compliance checkbox. It is a powerful, active capability available right now to protect not just names and accounts, but the most sensitive, proprietary aspects of your business.