
You don’t get to decide whether you want to enter this fight because you’re already right in the middle of it. Banks and enterprises are scrambling to figure out what to do with autonomous AI agents, agent swarms and hive minds. And the threat is not some theoretical scenario waiting for your executive team and risk committee to approve an annual roadmap.
The agents are already hitting your edge right now. They are scraping your applications, driving automated pipelines through customer accounts, and testing the seams in your firewalls and gateways. It’s not just the internal Shadow AI running on corporate laptops that you have to worry about. Even though that vulnerability is very real and sits inside your firewall, you also have to contend with the immediate and real danger coming from outside-in.
Attackers are already armed with autonomous software sitting on the public internet, acting with valid customer credentials, and already tearing down traditional defenses while pretending to be a living, breathing human being. They’re getting pretty damn good at the mimicking. And all the while, millions of consumers are signing up for agents and handing over the keys to make their lives easier.
This surge is overwhelming even the best-funded engineering teams. Look at the recent CNBC news on Bank of America. They’re a top-tier banking institution, with elite engineering talent, and they’ve spent billions on internal infrastructure and security controls that rival or exceed the hyperscalers. Yet even teams with those resources are feeling the strain, spooling up thousands of engineers just to shore up their legacy systems.
Someone remarked to me recently that this feels like our industry’s new Y2K moment, but that comparison falls apart instantly when you look at the engineering reality. Y2K was a trivial and finite problem to solve in comparison. What we are dealing with today is nothing like that. You cannot run a grep command to find where a non-deterministic probability engine is going to hallucinate, drift in its reasoning, or get tricked by an indirect prompt injection. You have brittle dependencies and unpredictable autonomous behavior scattered everywhere, and there is no massive pool of talent sitting on the sidelines who can magically patch that kind of bespoke complexity.
The industry’s counterattacks are already underway, and they are predictably relying on familiar playbooks. They are pushing high-friction controls like forcing a human into the loop, attempting to certify trusted agents, detecting bots at the edge, or throwing up semantic gateways and probabilistic firewalls. These are understandable approaches that lend value, but they are woefully inadequate against the perfect mimic and the machine-speed swarm.
The Perimeter is the Wrong Battlefield
Security leaders remain obsessed with trying to figure out whether the entity on the other end of the wire is a biological human or an automated agent.
That is an absolute dead end.
The models are evolving too fast, and the tools driving them are already past the point of casual detection. If your security strategy ultimately depends on measuring mouse jitter, checking canvas fingerprints, or throwing up CAPTCHAs, you are burning capital fighting an increasingly expensive detection war while completely missing the exposed flank.
Modern headless browsers paired with multi-modal models can emulate human typing cadence, non-linear cursor paths, and screen reading with terrifying accuracy. But even that misses the bigger issue. Real customers increasingly want agents acting on their behalf. They are deliberately handing their credentials, session access, and OAuth permissions to third-party agents so the software can pay their bills, manage their working capital, and optimize their yields. When the legitimate account holder handed over the keys on purpose, proving that the caller is a machine doesn’t actually solve your problem.
Trying to separate humans from machines at the perimeter is a losing game. The only viable path forward is to stop caring about the biological nature of the caller and build control systems that govern what the caller is actually permitted to do inside the system.
This requires understanding why traditional identity and authorization are fundamentally limited and insufficient for today’s threat. The industry has spent decades blurring the line between identity, authorization, and accountability, but they are entirely different animals. Identity simply tells you someone presented a valid credential. Authorization, whether you use role-based access or attribute-based access, just checks if a static permission flag is turned on. Neither one delivers accountability, and neither one protects a balance sheet from an agentic attack.
identity ≠ authorization ≠ permissions ≠ accountability
In legacy banking, identity worked as a decent security boundary partly because humans worked the process and human fallibility is narrow and containable. If an individual customer makes an honest mistake, an impulsive transfer, or an outright foolish financial choice, that failure stays locked inside that specific account. It can be ugly but it’s manageable. The bank writes off the loss, runs it through standard dispute paperwork, and moves on with its day.
Agents Change The Art of Defense
Agents destroy the entire economics of that model because they represent a correlated, choreographed, class-level failure. They share the same base foundation models, the same system prompts, the same orchestration libraries, and the same cloud platforms. When an autonomous financial agent suffers a reasoning failure or gets hijacked by an indirect prompt injection, it does not fail in isolation. It fails across ten thousand accounts at the exact same millisecond.
Identity tells you the user gave the agent permission. Authorization tells you the token has transfer rights. Neither one, on its own, stops a correlated machine-speed failure from draining liquidity, exposing sensitive information or creating systemic damage before a human operations team has even figured out what is happening. That is the accountability gap.
I saw the personal side of this shock-and-awe realization just a few days ago with a colleague. He was telling me how excited he was after installing Muse. He linked it directly into his personal email, handed it his calendar, and was thrilled about how much time it was going to save him by organizing his life. I do understand the value this can provide, but I looked at him and asked if he had any idea where his data was actually living now.
What happens when a malicious invoice lands in his inbox with white-on-white text that tells the agent to silently forward his correspondence to an external server? The user might never see this or know that anything is wrong. That’s the social engineering threat we’re seeing escalate with AI. Having spent years in offensive security and systems architecture, you learn that intimate access without hard and fine-grained controls is an open invitation for trouble … and identity theft. This colleague had handed broad, unattended execution power over his life to an external agent without any real limitation on what it could actually execute.
And this is not an isolated case. The same scenario happened recently in a large enterprise where a CoPilot agent was developed to improve productivity. It was a Shadow AI case where the agent consolidated email information and pulled highly sensitive data from file systems. It was a productivity win, but thankfully someone recognized immediately how dangerous that unattended access was before it blew up.
Now take that same blind trust and apply it to real money. The market is flooded with startups selling agents that promise to manage your accounts, rebalance your portfolio, and make you rich while you sleep. Handing your capital over to an autonomous agent without hard, adult supervision on every single transaction is asking for catastrophe. These massive probability machines are brilliant at syntax, but deploying them unconstrained is like handing your checkbook and your car keys to a junior intern with ADHD. They have no situational awareness of your real-world exposure, they do not understand counterparty risk, and they cannot pay attention long enough to realize they just kicked off a ruinous financial loop.
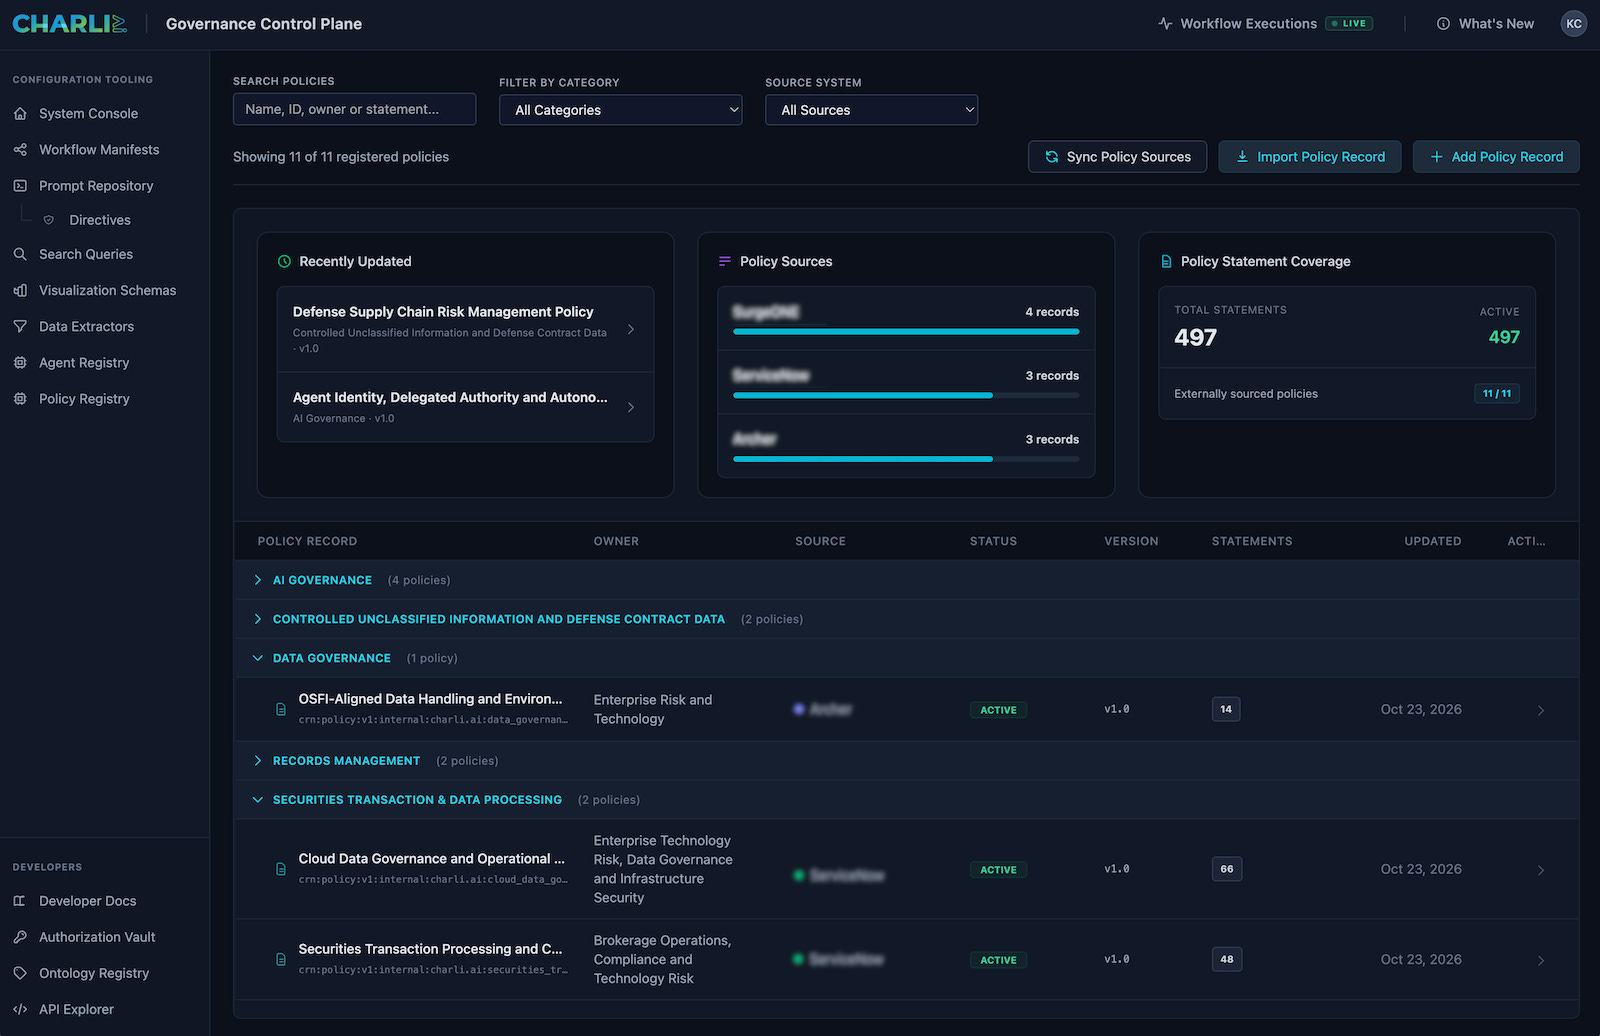
From the bank’s perspective, this is a legit nightmare. When a quarter-million-dollar transaction hits the wire, who’s on the other end of the button? Is it the customer? Is it an agent doing what the customer wanted? Is it an agent acting on a hallucinated inference? Or is it an agent executing instructions hidden inside a corrupted PDF three hops removed?
Who’s got accountability!
The standard reaction I get to this is frequent and unfortunately predictable. People constantly ask me: “Won’t OpenAI, Anthropic, or Meta just figure it out and fix this at the model level.” It’s a genuine head scratcher when everyone places trust in the Silicon Valley oligarchs that the media screams about almost every day.
The short answer is they will not … for many reasons. You never put faith in the application doing the thing to govern the thing itself. That self-policing prophecy has never worked in any serious industry, and in regulated enterprise environments it is flatly rejected.
Moreover, the consumer AI mindset does not match enterprise reality. A real enterprise does not depend on one frontier model. It runs on a mix of commercial models, open-source models, private models, internal software, SaaS applications, and a massive library of internal tools. A real enterprise has statutory Chinese walls between operating units and trading desks that cannot be left to the whims of a model’s prompt. Most importantly, a real enterprise holds highly sensitive proprietary data that can never, under any circumstance, leave its four walls just to ask an external AI company whether an action looks safe.
What is missing in this world of machine-speed swarms and automated execution is an independent, deterministic policy control layer that sits right at the wire. It’s fixated right in the path, and wired into the existing security controls your organization already relies upon.
So does that mean building another model to protect against a frontier model, or relying on a semantic filter?
Relying on semantic security by throwing smaller language models into the gateway to judge an action is a fatal mistake. You cannot defend against a probabilistic attacker by using a probabilistic defender. In fact, you are inadvertently increasing the attack surface and creating yet another vulnerability. There are lingering loopholes in that approach, to say nothing of the unacceptable latency it introduces into real-time transactional pipelines.
Semantic processing is a valuable tool for gathering telemetry and understanding context, but enforcement must be unyielding and deterministic. At the point where an action becomes real, the enterprise needs hard controls capable of evaluating the broader situation, not merely the identity of the caller or the scoped permissions or even the semantics of a single request. Those controls have to operate across aggregate activity, business context and current system state … and they have to operate at real machine speed.
Control
This is not another static rules engine checking whether a transaction falls below a threshold or whether a permission flag is turned on. Deterministic judgment means evaluating the requested action against the broader state of the system, including delegated authority, aggregate activity, business context and applicable policy, and arriving at an enforceable outcome without relying on another probabilistic model to make the final call.
It’s a zero-trust approach backed by a layer of deterministic policy control. External agents can think and plan whatever they want out on the public network, but once they attempt to interact and transact, the control plane must exercise hard, deterministic judgment to shut the gate. That judgment has to be far more contextually competent and situationally aware than standard security gateways, legacy firewalls, or semantic filters could ever hope to handle. It does not matter whether the caller is a human or an agent. The deterministic policy control layer becomes both the ultimate protector of the balance sheet and a foundational trust enabler for the business.
A scalable deterministic judgement, grounded in policy and current context, produces an attributable, reproducible record. That record is what accountability ultimately hangs on. And before you ask, deterministic judgement does not require another probabilistic model in the loop to establish situational awareness. That awareness can come from observable enterprise state and policy already available to the control plane.